Managed Security Operations

Automated security tools are essential for a modern defense posture, but they often generate an overwhelming volume of alerts, leaving internal IT teams buried in raw data. Our Managed Security Operations and CDR Analysis service cuts through the noise. We provide a dedicated team of human experts who continuously monitor, analyze, and tune your security logs and SIEM environment. Going beyond basic, automated monitoring, our analysts proactively hunt for hidden, sophisticated threats that are specifically designed to evade standard software defenses.
We eliminate the "alert fatigue" that frequently burns out internal IT and security personnel. By acting as your continuous first line of defense, our managed operations team filters out false positives and routine anomalies. We escalate only verified, high-priority threats with clear, actionable context. This ensures your internal staff can stop chasing false alarms and focus their limited time and resources where it matters most: driving your agency's mission forward and responding to genuine security events with precision and confidence.
Continuous Defense
Human experts continuously monitor, analyze, and tune your security logs and SIEM environment, then escalate only verified, high-priority threats.
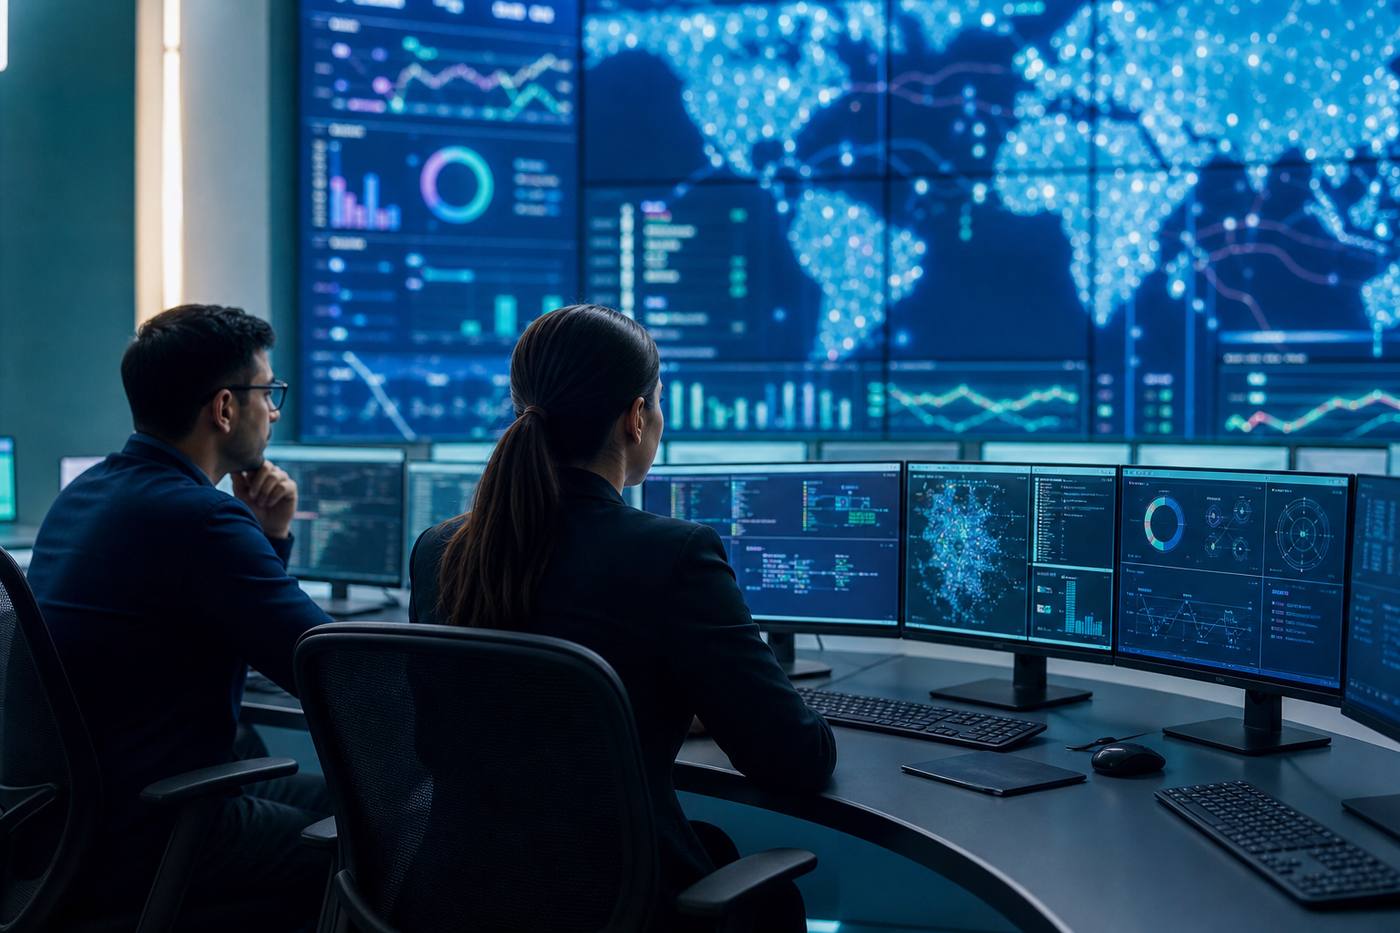
Managed operations and CDR analysis
A dedicated team of human experts continuously monitors, analyzes, and tunes your security logs and SIEM environment to cut through alert noise.
Proactive threat hunting
Analysts go beyond basic automated monitoring to hunt for hidden, sophisticated threats designed to evade standard software defenses.
Verified escalation, not alert fatigue
We filter false positives and routine anomalies, then escalate only verified, high-priority threats with clear, actionable context so your staff can focus on the mission.